Malware is learning to rank what it steals
A newly analyzed infostealer adds AI after the theft, using a language model to turn a pile of stolen data into a prioritized target profile. The important change is not how the malware gets in, but what happens next.
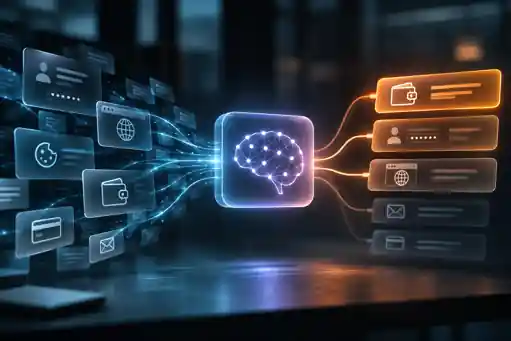 Editorial visualization
Infostealers have always had a sorting problem. A compromised machine can yield passwords, browser cookies, payment details, cryptocurrency wallets, email sessions and fragments of a person’s online life. Stealing the data is one task. Deciding which victim is worth pursuing first is another.
Cisco Talos says a newly analyzed infostealer called VOLTA adds a language-model stage to that second task. In research published October 31, 2026, Talos described an optional component that turns collected information into a structured assessment of the victim and ranks the assets that may be most valuable to an attacker.
The AI arrives after the theft
That distinction matters. VOLTA is still an infostealer first: its core job is to collect credentials, active sessions and other sensitive information from an infected machine. The AI component does not replace the initial compromise. It analyzes what has already been gathered.
Talos says the malware can assemble a dossier from multiple categories of stolen data and send that bundle to commercial language models for analysis. The requested output is closer to an intelligence brief than a raw dump: a profile of the victim, an assessment of their likely value and a prioritized view of the accounts or assets worth attention.
WIRED, which reported on the Talos findings the same day, noted an important limit: Talos had not confirmed that VOLTA had been used in real-world attacks. That means the discovery is evidence of a capability built into malware, not proof that the technique is already widespread.
Why prioritization changes the economics
A large theft can create its own bottleneck. Stolen credentials and session tokens are time-sensitive: passwords can be changed, sessions can expire and defenders can revoke access. Human operators have to decide where to spend attention while that window is still open.
Automated triage shifts some of that work from the operator to the model. The result is not necessarily a more capable intrusion technique. It is a faster way to convert messy stolen information into a shortlist of targets and next actions. That can make an existing criminal workflow more efficient, especially for operators who lack the staff or expertise to inspect every victim manually.
The pattern is broader than one malware family. In its September 2026 threat report, Anthropic said it had observed AI reducing the labor and specialist knowledge required for several kinds of cyber operations, from reconnaissance and tool development to processing stolen data. The company argued that the traditional link between operational sophistication and a sophisticated human team is becoming less reliable.
The defensive lesson is less glamorous
For defenders, the useful takeaway is not that every attacker now has an autonomous cyber agent. It is that the value of stolen access can be extracted faster. Controls that shorten the useful life of stolen credentials and sessions therefore matter even more: rapid password resets after compromise, session revocation, strong multi-factor authentication, endpoint detection and limiting how much a single account can reach.
The same logic applies to the data left inside ordinary accounts. Email receipts, saved sessions and cloud dashboards can reveal identity, spending, work relationships and access patterns when combined. Individually mundane records become more useful when a model can summarize them quickly and connect them across services.
VOLTA is notable because it makes that analysis step explicit. The malware still needs a victim, stolen data and an attacker willing to act on the result. What AI changes is the amount of human effort required between collection and decision.
That is a narrower claim than saying AI has reinvented cybercrime, but it is also more consequential. The next competitive advantage for attackers may not come from stealing more information. It may come from deciding, faster than before, which stolen information deserves attention.
Publication history
— First published.
No published corrections or earlier versions.
How this was made
UpThat uses AI-assisted research and writing. Source checking and publication follow our editorial review workflow. See the original documents above to assess the reporting.
How we use AI ↗